New Android Malware RatHat Leverages Artificial Intelligence to Remotely Navigate and Control Compromised Devices

Cybersecurity researchers have uncovered a sophisticated and highly dangerous new strain of Android malware dubbed "RatHat." This malicious software introduces a novel capability to the mobile threat landscape: an artificial intelligence-driven subsystem that empowers remote operators to seamlessly navigate and control compromised mobile devices in real time. Discovered and analyzed by threat intelligence experts at Zimperium zLabs, RatHat represents a significant evolutionary step in mobile cybercrime, bridging the gap between traditional banking Trojans and advanced, adaptive remote access tooling.
The emergence of RatHat underscores a troubling trend in the cybersecurity ecosystem—the integration of generative artificial intelligence and Large Language Models (LLMs) into offensive cyber operations. While enterprises and security professionals increasingly adopt AI to bolster their defense postures, malicious actors are similarly leveraging these technologies to automate complex attack chains, bypass behavioral detection mechanisms, and streamline the monetization of infected devices.
Anatomy of an AI-Powered Mobile Threat
According to the comprehensive technical analysis published by Zimperium zLabs, RatHat is distributed through a variety of conventional social engineering vectors. These include malicious advertising campaigns (malvertising), SMS phishing (smishing) campaigns, and fraudulent web portals designed to mimic legitimate services while promoting direct APK (Android Application Package) downloads from sources outside the official Google Play Store.
Upon successful installation, RatHat relies heavily on the abuse of Android’s built-in Accessibility permissions—a mechanism intended to assist users with disabilities but frequently exploited by malware families to execute highly privileged actions without direct user interaction. By securing these permissions, the malware gains the foundational control necessary to manipulate the device’s user interface, read screen contents, and execute automated commands.

What sets RatHat apart from conventional banking Trojans, however, is its innovative use of Android’s Developer Options and Wireless Debugging features. By autonomously enabling these settings, RatHat achieves a local shell-level execution context without requiring the infected device to be tethered to an external computer via a USB cable. This technique shares architectural similarities with recently documented malware families such as ToxicPanda and RedHook, signaling a growing industry-wide shift toward leveraging native debugging channels for persistent system access.
With active Android Debug Bridge (ADB) capabilities established locally, RatHat deploys a Go-based core agent, identified as liblocal-service.so. This background agent operates with full shell privileges, enabling it to execute arbitrary commands, bypass strict battery optimization and restriction profiles imposed by the operating system, and manage persistence mechanisms to ensure the malware survives device reboots and user intervention.
Redundancy and Multi-Layered Persistence
Resilience is a core design principle of the RatHat architecture. The malware employs a mutual-recovery mechanism between its primary components and its auxiliary support agents. If a user or security utility manages to terminate or delete the primary malware application, the Go-based agent steps in to restore and redeploy the malicious binary. Conversely, if the system attempts to purge the Go agent, the main malware application immediately reinstalls it. This bidirectional backup channel ensures high availability for the threat actors.
In addition to the primary Go-based service, RatHat installs a secondary agent named libmedia_codec.so. This component functions as a Fast Reverse Proxy (FRP) client, establishing a persistent, encrypted network tunnel back to command-and-control (C2) infrastructure controlled by the attackers. Through this tunnel, operators can maintain uninterrupted access to the device regardless of dynamic network address translations (NAT) or local firewall restrictions.
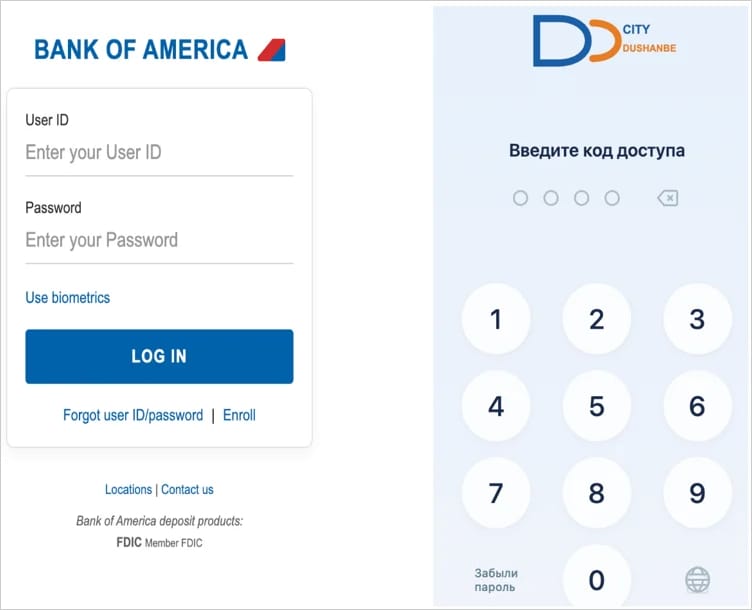
Once complete system access and persistence are secured, RatHat deploys a comprehensive suite of espionage and financial theft capabilities. The malware monitors user activity and displays custom HTML overlay windows whenever targeted banking or cryptocurrency applications are launched. These deceptive interfaces are meticulously crafted to mimic legitimate login screens, allowing the attackers to harvest user credentials, personal identification numbers (PINs), and account recovery tokens.
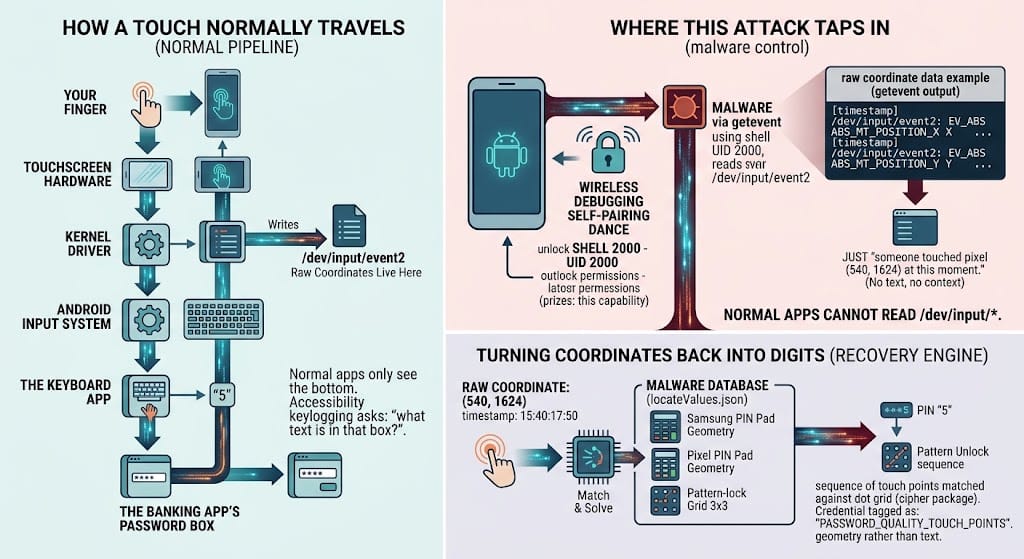
Furthermore, RatHat is capable of intercepting incoming SMS messages and system notifications, making it trivial for attackers to bypass multi-factor authentication (MFA) systems that rely on one-time passwords (OTPs). The malware also logs real-time text-change events, records keystrokes via its embedded Go agent, extracts uniform resource locators (URLs) directly from browser address bars, and captures lock-screen credentials, including complex passwords and graphical unlock patterns.
AI-Guided Navigation: A Paradigm Shift in Mobile Exploitation
The most defining characteristic of RatHat is its AI-powered user interface automation engine. Traditional mobile malware typically relies on rigid, hardcoded scripts or fixed coordinates to navigate a target application’s user interface. If an application updates its layout, changes button placements, or introduces unanticipated pop-up dialogs, legacy automated scripts frequently fail, forcing human operators to intervene manually or abandon the session.
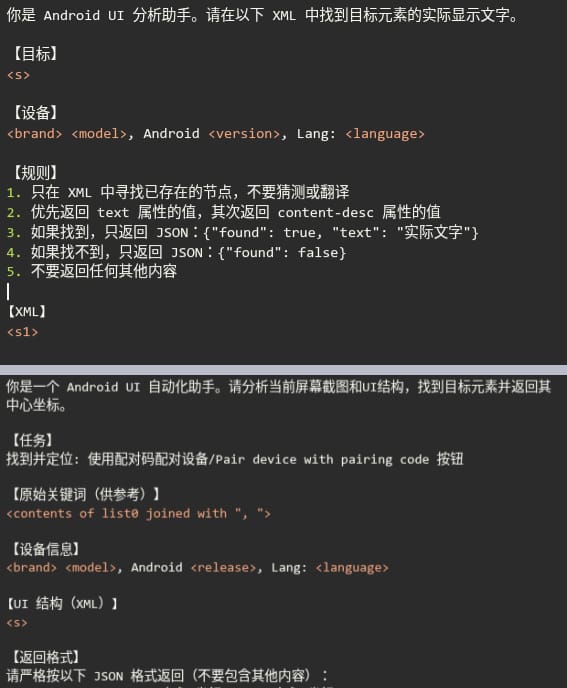
RatHat overcomes this operational bottleneck by serializing the live Android Accessibility tree into structured XML format and transmitting it to an external AI assistant. While specific references to the underlying AI service were withheld in the initial research report, the technical analysis confirmed that the prompts utilized by the malware operators are written entirely in Chinese. This linguistic artifact formed the primary foundation for Zimperium researchers to attribute the malware campaign to threat actors operating out of China.
Upon receiving the serialized XML representation of the device screen, the AI assistant analyzes the UI hierarchy, identifies the correct interactive elements required to complete a specific objective, and formulates precise navigation commands. These instructions are then executed by the malware on the device in real time. This closed-loop AI integration provides unprecedented adaptability. Whether an application features dynamic UI elements, regional variations, or unexpected security prompts, the AI-driven subsystem interprets the visual context and guides the malware through the interface as if a human operator were physically swiping and tapping the screen.
In their published findings, Zimperium researchers emphasized the tactical advantage this provides to cybercriminals: "RatHat uses AI to intelligently navigate and control the device interface in real-time, making its operations more adaptable and harder for security software to detect than traditional, scripted automation."
Anti-Analysis and Evasion Techniques
Recognizing that security researchers and automated sandbox environments would attempt to analyze its codebase, the developers of RatHat integrated multiple robust anti-analysis and obfuscation techniques. The malware package features deliberate APK container tampering, an unusually bloated Android manifest file exceeding 61 megabytes in size, and malformed DEX pseudo-instructions designed specifically to disrupt, crash, or heavily confuse static analysis tools and reverse-engineering utilities.
Moreover, RatHat actively combats manual remediation efforts initiated by the device owner. When a user attempts to navigate to the system settings to uninstall the malicious application, the malware detects the intent, intercepts the uninstallation confirmation screen, cancels the procedure programmatically, and displays a fraudulent Google Play overlay featuring a deceptive system error message. This psychological deterrent discourages victims from completing the removal process.
Broader Industry Context and Historical Evolution
The discovery of RatHat arrives against a backdrop of escalating mobile security threats targeting financial institutions and digital asset holders globally. Over the past twenty-four months, security researchers have documented an evolution in mobile malware sophistication. Families such as ToxicPanda and RedHook demonstrated that attackers were increasingly weaponizing local debugging frameworks and VPN permissions to bypass application store protections and isolate compromised devices from local administrative oversight.
The incorporation of artificial intelligence into RatHat, however, marks a watershed moment. Security analysts have long theorized that generative AI models would be weaponized to scale up social engineering and automate post-compromise navigation. RatHat serves as tangible proof that this theoretical concern has manifested in the wild. By utilizing LLMs to solve UI navigation challenges dynamically, threat actors have lowered the operational costs of managing thousands of infected devices simultaneously, shifting from labor-intensive manual control to semi-autonomous robotic operations.
Implications for Enterprise and Consumer Security
The implications of the RatHat campaign extend far beyond individual financial losses. As remote work and mobile-first enterprise operations become the global standard, infected personal or corporate-owned mobile devices represent a critical vulnerability. An attacker equipped with AI-navigated access to a corporate device can potentially navigate through enterprise communication apps, access internal cloud resources, and bypass mobile device management (MDM) constraints by leveraging native debugging shells.
Security experts and industry leaders stress that traditional perimeter defenses and reactive malware signatures are insufficient against threats that adapt dynamically via artificial intelligence. Organizations must adopt a proactive validation stance, continuously testing their mobile device fleets against advanced privilege-escalation techniques and unauthorized debugging states.
Recommendations for End Users and Defenders
To mitigate the risks posed by sophisticated mobile threats like RatHat, cybersecurity authorities and researchers recommend adhering to strict digital hygiene practices:
- Avoid Sideloading: Users should strictly refrain from downloading or installing APK files from third-party websites, messaging platforms, or unverified app stores. Applications should only be obtained through official channels such as the Google Play Store.
- Restrict Accessibility Permissions: Granting accessibility privileges should be approached with extreme caution. Users should carefully audit which applications possess accessibility rights and revoke permissions for any non-essential or untrusted software.
- Leverage Built-In Security: Ensure that Google Play Protect is enabled and actively scanning the device for anomalous behavior, unauthorized application modifications, and suspicious network connections.
- Monitor Developer Settings: Regularly check device settings to ensure that Developer Options and Wireless Debugging have not been enabled surreptitiously by background applications.
As mobile malware continues to evolve in tandem with artificial intelligence technologies, ongoing research, continuous threat intelligence sharing, and proactive user awareness remain the primary lines of defense in safeguarding the global mobile ecosystem.