DDRop: Researchers Uncover Hardware Interposer Attack Compromising Intel and AMD Confidential Computing

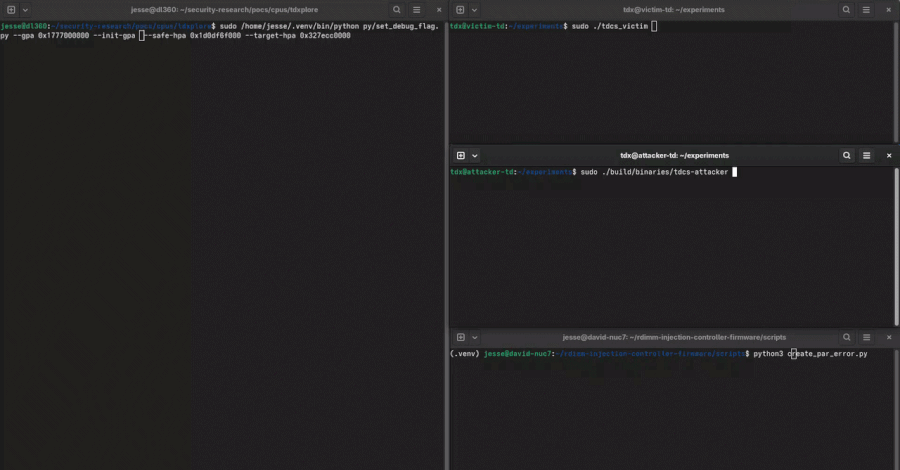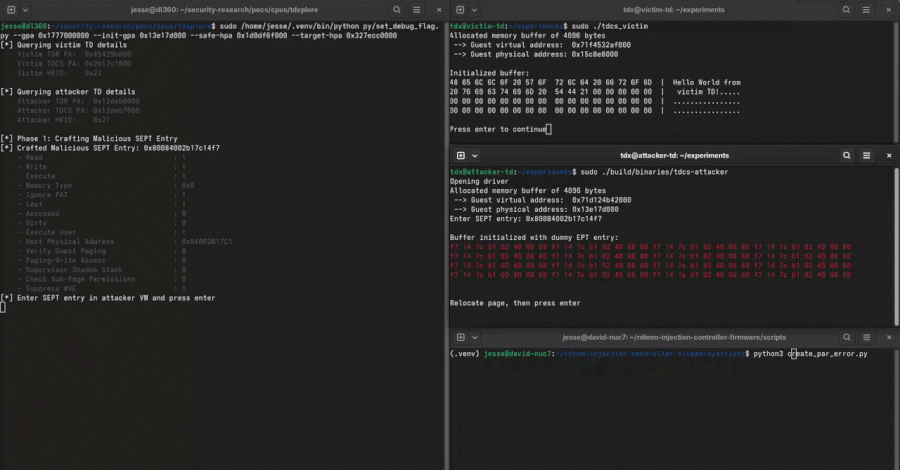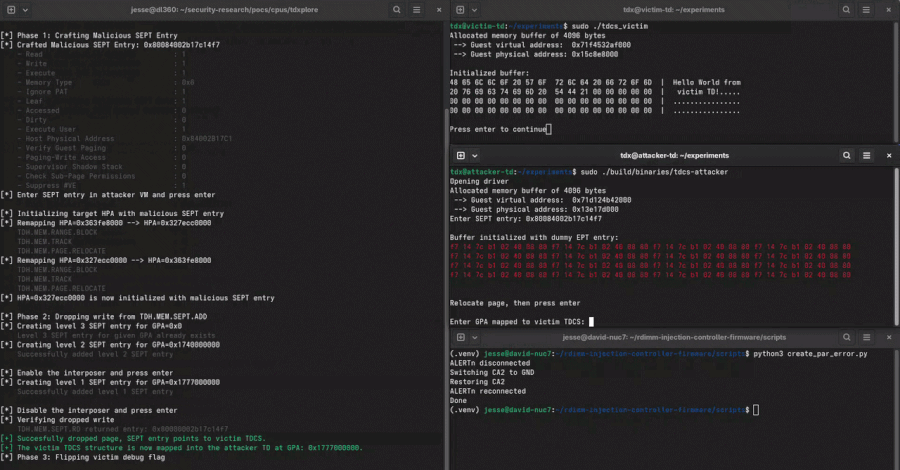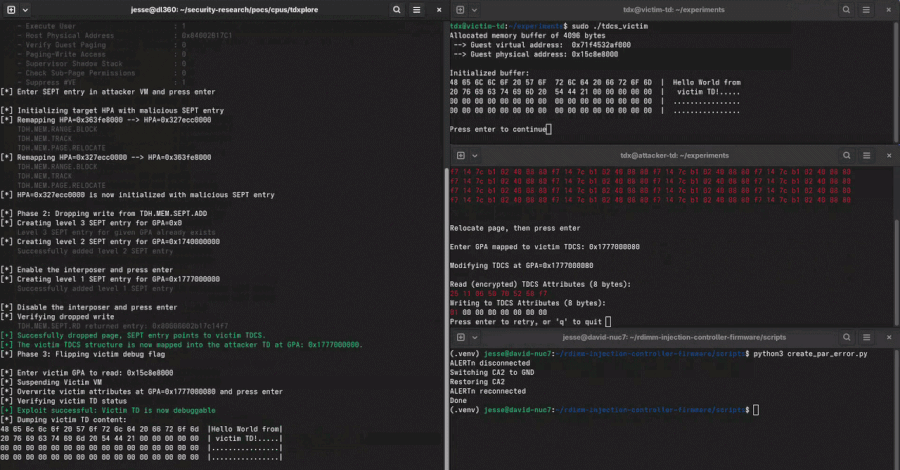
The landscape of cloud-based data security faces a significant challenge following the disclosure of a novel hardware-based attack dubbed DDRop. This vulnerability targets the foundational security promises of "confidential computing"—a technology marketed by industry giants like Intel, AMD, and major cloud service providers (CSPs) as the gold standard for protecting data while it is in active use. By exploiting a fundamental design limitation in memory encryption, researchers have demonstrated that a relatively inexpensive hardware device can bypass critical integrity protections, allowing an attacker to manipulate server memory without detection.
The Mechanism of DDRop
At its core, DDRop is an active interposer attack that operates at the physical layer of a server’s memory architecture. Unlike software-based exploits that rely on code vulnerabilities or side-channel leakage, DDRop requires physical access to a machine to install a small, custom-built circuit board between the processor and the DDR5 memory module.
The attack exploits the "freshness" gap in current confidential computing implementations. While technologies such as Intel’s Trust Domain Extensions (TDX) and Scalable SGX, as well as AMD’s Secure Encrypted Virtualization-Secure Nested Paging (SEV-SNP), provide robust encryption for data at rest in RAM, they often lack a mechanism to verify that the data being read is the most recent version written by the processor.

The DDRop interposer functions as a "man-in-the-middle" on the memory bus. It runs at full DDR5 speeds, monitoring commands between the CPU and the memory. When it identifies a specific write operation, it injects an error into the command bus and simultaneously severs the wire responsible for reporting that error back to the memory controller. As a result, the memory module silently discards the update, leaving the old, encrypted data intact. Because the processor’s encryption engine does not perform a freshness check, it treats the stale data as the current, valid value, effectively allowing the attacker to "roll back" memory states or inject stale, malicious instructions.
Chronology and Development
The research, a collaborative effort involving experts from KU Leuven, ETH Zurich, Durham University, and Google, is slated for formal presentation at the ACM CCS 2026 conference this November. The path to this disclosure involved several years of iterative testing against evolving memory standards.
- Early 2025: Research into passive interposer attacks like "TEE.fail" demonstrated the ability to eavesdrop on memory buses, though these were constrained by the need for lab-grade equipment and slower clock speeds.
- Mid-2025: The "Battering RAM" attack emerged, targeting DDR4 memory via address-swapping. However, the architectural shift to DDR5 rendered these earlier techniques obsolete, as the new command format blocked traditional manipulation methods.
- Late 2025 – Early 2026: The DDRop team pivoted to a write-dropping methodology. By developing a specialized, low-cost ($159 in parts) interposer, they successfully bypassed DDR5’s protections.
- August 2026: Coordinated disclosure protocols were initiated. Intel and AMD were briefed on the vulnerability to allow for security bulletins, though both corporations have maintained that such attacks fall outside their defined threat models.
Technical Implications for Intel and AMD
The severity of DDRop varies depending on the hardware platform. On Intel TDX systems, the researchers achieved full control over protected virtual machines (VMs). By dropping writes during the initialization of page tables, the attackers could force the system to map memory to attacker-controlled addresses. This provided a gateway to read private memory, toggle debug modes, and even forge the "launch measurements" that customers rely on to verify the integrity of their cloud instances.
For AMD SEV-SNP, the impact is described as more constrained. While the researchers successfully utilized write-dropping to copy data between pages, the more advanced debug-mode and attestation-forgery attacks were specific to the architecture of Intel TDX. However, the researchers emphasize that because the root cause—the lack of a freshness check—is universal across these platforms, no current implementation is immune to the fundamental logic of the attack.

Older iterations of Intel’s SGX, which utilized a hardware integrity tree, are notably immune to this specific vulnerability. However, Intel has largely moved away from that architecture in favor of the more scalable, yet "freshness-deficient," encryption models used in modern server-grade CPUs. NVIDIA’s confidential-computing GPUs are currently deemed unreachable by this specific hardware attack, as their memory is tightly integrated within the chip package, precluding the insertion of an interposer.
Official Responses and Industry Stance
Both Intel and AMD have issued formal responses emphasizing that DDRop requires physical access to the server hardware. In the cybersecurity industry, physical access is frequently categorized as an "out-of-scope" threat for cloud-based threat models, as data centers are generally protected by multiple layers of physical security.
AMD stated that the attack "falls outside the scope of the published threat model for SEV / SNP." Intel has echoed this sentiment, noting that it does not plan to issue a Common Vulnerabilities and Exposures (CVE) identifier for the attack. Despite this, both companies are reportedly working on future hardware iterations that incorporate more robust integrity and freshness checking. Intel has pointed to "cache-line versioning" as a potential path forward, though researchers remain skeptical about whether such a solution would be sufficient to neutralize the DDRop methodology.
Broader Impact on Confidential Computing
The existence of DDRop underscores a growing tension in high-performance computing: the trade-off between performance and absolute integrity. Maintaining a freshness check on every memory transaction adds significant latency and overhead, which would diminish the appeal of confidential computing for high-speed, enterprise-level workloads. By prioritizing speed, vendors have effectively left the door open for physical-layer attacks.

The threat posed by DDRop is not merely theoretical. While the researchers noted that there is no evidence of the attack being used in the wild, the low cost and relative simplicity of the hardware interposer make it a plausible tool for sophisticated threat actors. The potential for a "rogue insider" in a data center or a supply-chain interdiction creates a realistic vector for exploitation.
Future Mitigation Strategies
Because the weakness is rooted in hardware design rather than software code, there is no "patch" that can definitively neutralize DDRop. Instead, industry experts suggest a "defense-in-depth" approach:
- Hardware Hardening: Future server designs must integrate cryptographic freshness checks directly into the memory controller. This would ensure that even if a write is dropped or a bus is tampered with, the system would detect the inconsistency and halt operations.
- Physical Security Audits: CSPs must enhance their physical infrastructure, potentially employing tamper-evident seals on memory modules and implementing more rigorous screening processes for employees with physical access to server racks.
- Software-Level Verification: While not a complete fix, software can implement additional checks to verify that critical data has been successfully written to memory. This increases the complexity of the attack but does not address the underlying architectural flaw.
- Boot-time Integrity: Systems could potentially be configured to scan for anomalous hardware signatures on the memory bus during the boot process, identifying the presence of an interposer before the system begins processing sensitive data.
The DDRop vulnerability serves as a stark reminder that as security software becomes more sophisticated, attackers will inevitably move down the stack toward the physical hardware. For the cloud industry, the focus must shift from solely encrypting data to ensuring the absolute integrity of the memory lifecycle. Until such time as processors can verify both the confidentiality and the "freshness" of memory data, the hardware-bus interposer will remain a potent weapon for those capable of gaining physical proximity to the world’s most sensitive server infrastructure.