Cybersecurity breach at Thai broadband provider 3BB exposes critical network vulnerabilities through the abuse of legitimate management tools

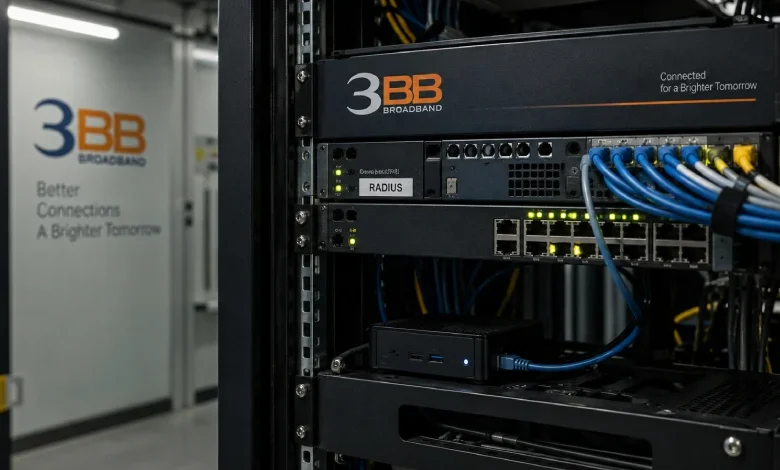
An sophisticated cyber intrusion into the infrastructure of 3BB, one of Thailand’s most prominent broadband service providers, has highlighted a growing and dangerous trend in modern cyber-espionage: the weaponization of legitimate administrative software to mask malicious activity. Threat intelligence firm Hunt.io recently disclosed that an unidentified threat actor successfully established a persistent presence within 3BB’s internal network, utilizing MeshCentral—a standard remote-management utility—to maintain deep-level access to critical systems. The discovery, which came to light after researchers stumbled upon an exposed server left online by the attackers, underscores the fragility of telecommunications infrastructure and the persistent threat posed by actors targeting sensitive subscriber data.
Chronology of the Discovery
The incident was identified on June 3, 2026, when Hunt.io researchers uncovered a misconfigured, publicly accessible server. This server served as the attacker’s operational hub, containing a repository of malicious scripts, internal reconnaissance data, and a comprehensive list of machines already compromised within the 3BB corporate ecosystem.
At the time of the discovery, the operation was active. Forensic analysis of the server revealed that the attacker had been systematically moving through the 3BB network, escalating privileges to the root level on multiple internal machines. The presence of the MeshCentral agent, configured as a hidden backdoor, confirmed that the threat actor had been maintaining stable, remote control over these assets. The command-and-control (C2) infrastructure was traced to the domain ayuthayatech[.]com, with the compromised devices categorized under a specific management group labeled "TH-3BB."

The Weaponization of Trust
The choice of MeshCentral by the threat actor is emblematic of a broader shift in adversary tactics. Rather than relying on custom-built, signature-heavy malware that might be easily flagged by endpoint detection and response (EDR) systems, modern attackers are increasingly leveraging "Living off the Land" (LotL) techniques. By utilizing trusted, industry-standard administrative tools, attackers can effectively blend in with routine network traffic, making detection significantly more difficult for security operations centers (SOCs).
In the 3BB incident, the attacker ensured that their presence was not only persistent but also stealthy. A specialized cleanup script was identified on the server, designed to systematically purge system logs and remove secondary exploitation tools, while deliberately leaving the MeshCentral agent intact. This strategic "pruning" of the digital footprint allowed the attacker to minimize the chances of discovery while maintaining a reliable "God-mode" access to the provider’s infrastructure.
The Scope of the Intrusion
The investigation revealed that the threat actor’s ambitions were not limited to simple system compromise. Once inside, the attacker engaged in an aggressive campaign of lateral movement and data harvesting. Using automated scripts, the adversary performed password spraying attacks against at least 55 internal computers via SSH. Furthermore, the attacker probed 3BB’s internal sales portal (agent.3bb.co[.]th) and scoured compromised machines for high-value intelligence, including stored database credentials, administrative SSH keys, and system configuration files.
Perhaps most concerning was the targeting of RADIUS databases. These systems are the backbone of broadband authentication, storing the login credentials that enable subscribers to access the internet. While Hunt.io noted that they found evidence of the databases being targeted, they stopped short of confirming that a mass exfiltration of customer credentials had occurred. However, the intent to target such sensitive information suggests a high-level strategic interest in compromising the confidentiality of 3BB’s massive subscriber base.

Furthermore, the discovery of a valid VPN certificate and active sessions associated with the Jasmine network—an entity with which 3BB shares historical and infrastructural ties—indicated that the breach potentially extended beyond the primary target. This suggests that the attackers were engaged in a "supply chain-style" reconnaissance, seeking to leverage the interconnected nature of the regional telecommunications ecosystem to expand their reach.
Analysis of the Initial Access Vector
While the exact method of initial entry remains unconfirmed, the recovered toolkit provided a chilling glimpse into the attacker’s capabilities. The server contained a fully functional exploit kit targeting a specific vulnerability in 3BB’s FortiGate SSL-VPN gateways. The kit specifically addressed CVE-2024-21762, a critical security flaw identified in 2024 that allows unauthenticated remote code execution.
The presence of this exploit, coupled with the fact that the targeted gateways were running firmware versions vulnerable to the flaw, presents a strong circumstantial case for how the perimeter was breached. However, from a forensic standpoint, the researchers noted that the tooling was as much a testament to the attacker’s intent as it was to their capability. The sophistication required to assemble such a targeted arsenal indicates a highly motivated and skilled adversary, potentially backed by significant resources.
Broader Implications for Telecommunications
The 3BB incident is a stark reminder of the unique risks facing telecommunications providers. These organizations hold the keys to critical national infrastructure, making them prime targets for state-sponsored actors and cyber-criminal syndicates alike. The ability to intercept traffic, monitor user activity, or disrupt service on a national scale provides attackers with significant geopolitical and economic leverage.

The abuse of remote-management software, as seen in this case, necessitates a paradigm shift in how security teams monitor their administrative environments. Traditional security models that focus on blocking known malware are no longer sufficient when the tools being used are, by design, intended for legitimate administrative functions. Defenders must now prioritize behavioral analysis, monitoring for unauthorized instances of management tools and unusual administrative patterns that deviate from established IT workflows.
Official Responses and Mitigation
Upon concluding their investigation, Hunt.io adhered to responsible disclosure protocols, notifying both the affected entities and the relevant national cybersecurity response teams in Thailand. The prompt disclosure was intended to provide 3BB and its partners with the necessary intelligence to purge the attackers and secure their perimeters before the findings were made public.
For organizations operating similar critical infrastructure, the recommendation from the security community is clear:
- Perimeter Hardening: Immediately patch all edge devices, specifically focusing on VPN and firewall appliances, and disable unused management interfaces.
- Behavioral Baselining: Implement strict monitoring for administrative tools such as MeshCentral, TeamViewer, or AnyDesk. Any instance of these tools that does not correlate with a known, approved IT ticket should be treated as a critical security incident.
- Credential Rotation: Given the attacker’s focus on harvesting SSH keys and database logins, a comprehensive, network-wide reset of privileged credentials is essential to ensure that any persistent access the attacker may have retained is invalidated.
- Network Segmentation: Limit the ability of internal machines to communicate with one another unless explicitly required for business functions, preventing attackers from easily moving laterally after an initial compromise.
Conclusion
As of the latest reports, the exposed server has been taken offline, and the threat actor has effectively gone to ground. Whether the attacker still maintains access to the 3BB network remains an open question—one that highlights the persistent nature of such intrusions. While the immediate threat may have been mitigated through the discovery and notification process, the incident serves as a crucial case study in the necessity of rigorous infrastructure hygiene. In an era where digital borders are increasingly porous, the security of providers like 3BB remains a matter of national interest, requiring constant vigilance, advanced threat hunting, and an evolving understanding of how attackers leverage our own tools against us.