Critical Security Vulnerability in Elementor Plugin Allows Unauthenticated Account Creation and Total Site Compromise

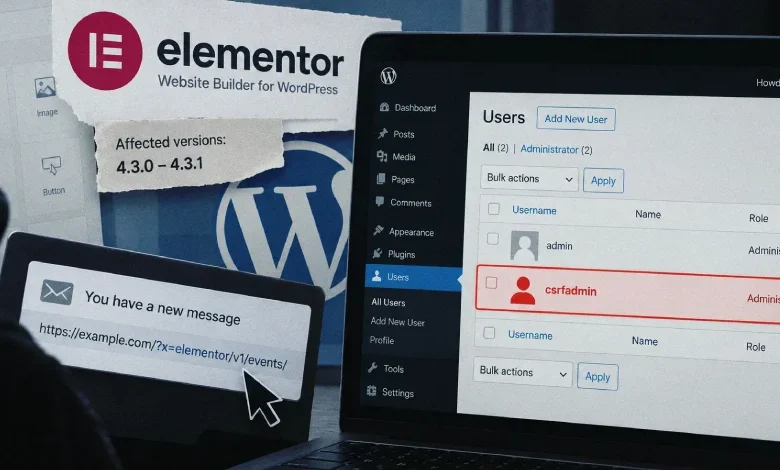
A high-severity security flaw recently discovered within the Elementor Website Builder plugin for WordPress has sent shockwaves through the web development community. The vulnerability, which carries a CVSS score of 8.8 out of 10.0, provides a gateway for unauthenticated attackers to perform unauthorized actions, including the creation of rogue administrator accounts, effectively granting them full control over affected websites. With Elementor serving as a foundational tool for over 10 million websites globally, the discovery of this flaw—specifically affecting versions 4.3.0 and 4.3.1—highlights the precarious nature of supply chain security in the modern web ecosystem.
The vulnerability is categorized as a Cross-Site Request Forgery (CSRF). Unlike more complex exploits that require sophisticated server-side injection or specific environmental configurations, this flaw is alarmingly simple to trigger. It requires only that a logged-in user with high-level privileges—such as an administrator—clicks a malicious link. Once clicked, the browser executes a REST API request on the user’s behalf, bypassing traditional security barriers.
Technical Analysis of the Flaw
The root of the issue lies within the Editor Events module, a feature introduced in recent versions of the plugin. According to research conducted by the security firm Patchstack, the module was designed to process certain REST API requests by evaluating the request URI. However, the implementation contained a critical logic error: it essentially opted out of CSRF protection whenever the string "elementor/v1/events/" appeared anywhere in the URL.
Because the request URI includes the query string, an attacker can append this specific string as a harmless-looking parameter to any legitimate REST API call. This effectively blinds the security check, allowing the request to bypass the standard authentication protocols intended to prevent CSRF. By manipulating the REST API surface—which includes not only WordPress core routes but also the routes of every other installed plugin—an attacker can execute arbitrary administrative functions. The most damaging of these is the ability to create a new user with the "administrator" role via the /wp/v2/users endpoint, providing the attacker with permanent, high-level access to the site’s backend.
Chronology and Disclosure
The timeline of this vulnerability reflects the standard procedures of responsible disclosure in the cybersecurity industry. The flaw was identified by a security researcher operating under the alias "Saggre." Upon discovering the bypass mechanism in the Editor Events module, Saggre alerted the Elementor development team.
Following a period of investigation and remediation, Elementor released version 4.3.2 earlier this week. This update specifically patches the logic error, ensuring that the CSRF protection is correctly applied regardless of the contents of the URI query string. Versions prior to 4.3.0 are unaffected because they did not incorporate the vulnerable Editor Events proxy. However, for the millions of sites that updated to the 4.3.0 or 4.3.1 releases, the risk remains acute until the latest security patch is applied.
Scope of the Threat
The scale of this issue is significant. Statistics from WordPress.org indicate that the two vulnerable versions alone are currently active on more than 2 million websites. When considering the ubiquity of Elementor—which powers everything from small personal blogs to large-scale enterprise e-commerce platforms—the potential attack surface is vast.

What makes this vulnerability particularly dangerous is the ease of execution. Attackers do not need to host malicious websites or distribute complex malware packages. The malicious link can be hidden as a simple hyperlink within a phishing email, a chat message, or even a comment section on a forum. When an unsuspecting administrator clicks the link, the attack happens in the background, often without any visible indication to the user that their site’s security integrity has been compromised. The attacker, having successfully created a new administrative account, can then proceed to install backdoors, inject malicious scripts, redirect traffic to phishing sites, or exfiltrate sensitive database information.
Industry Context and Web Security Implications
The Elementor incident serves as a stark reminder of the "plugin dependency" risks inherent in the WordPress ecosystem. WordPress powers approximately 43% of all websites on the internet, and a vast majority of these sites rely on third-party plugins to provide core functionality. While this modularity drives innovation and ease of use, it also creates a complex web of dependencies where a single vulnerability in a widely used plugin can jeopardize millions of digital assets simultaneously.
Cybersecurity analysts have long warned about the "REST API attack surface." As WordPress continues to modernize its core architecture by moving toward a more API-driven structure, developers must ensure that security measures are not just present, but resilient to bypass techniques. The mistake of using simple string matching to exclude security checks is a classic example of an "implementation flaw," where the intended security policy fails due to an oversight in the underlying code logic.
Expert Recommendations and Mitigation
For site administrators and web developers, the primary defense against this vulnerability is immediate patching. The following steps are recommended:
- Immediate Update: All sites running Elementor versions 4.3.0 or 4.3.1 must be updated to version 4.3.2 or higher immediately.
- Audit Administrative Accounts: Administrators should review their user list for any unauthorized accounts, especially those created recently. If suspicious accounts are found, they should be deleted immediately, and password resets should be initiated for all legitimate administrators.
- Enhance Access Controls: While not a direct fix for this CSRF, implementing Multi-Factor Authentication (MFA) for administrative accounts can mitigate the impact of account hijacking, as an attacker would require a second form of authentication to gain entry even if they create a new user account.
- Monitor REST API Activity: Using security plugins that monitor and log REST API requests can help administrators identify unusual traffic patterns that might indicate an attempted exploit.
- Principle of Least Privilege: Ensure that accounts used for daily management do not possess higher privileges than necessary. If an account does not need administrative access to function, it should be downgraded to "Editor" or "Contributor."
Looking Ahead
The disclosure of this vulnerability highlights the necessity of robust security testing during the software development lifecycle. As Elementor and other major plugin developers continue to release frequent updates to remain competitive, the pressure to deliver new features must not come at the expense of security rigor.
The security community has praised the swift response from the Elementor team, as the availability of a patch within days of the reported issue helps to minimize the "window of exposure." However, the challenge remains in the "long tail" of web management—the thousands of sites that may remain unpatched for weeks or months due to neglected maintenance or a lack of administrative oversight.
As the digital landscape becomes increasingly targeted, the responsibility for security is shared between the software vendors and the site owners. While vendors must provide secure code, owners must adopt a proactive stance on maintenance, ensuring that their sites are not just functional, but hardened against the evolving threats of the modern web. The Elementor case will likely be studied as a textbook example of how a seemingly minor logic error can lead to a systemic security threat, underscoring the vital importance of secure coding practices in the plugin development industry.
Related posts: