OpenAI Codex Sandbox Vulnerabilities Exposed Developers to Remote Code Execution via Malicious Repositories

Security researchers have uncovered two critical sandbox evasion vulnerabilities in OpenAI’s Codex coding agent, including a severe flaw capable of executing arbitrary commands on a developer’s local machine without user approval or visual indicators. The discovery highlights the mounting cybersecurity challenges associated with integrating powerful autonomous artificial intelligence agents directly into local development environments.
The vulnerabilities, collectively demonstrated by researcher Oren Yomtov of Accomplish AI, target the core architectural boundaries of Codex, which operates as both a command-line interface (CLI) tool and a desktop application. These security gaps allowed malicious code originating from untrusted software repositories to bypass restrictive security parameters and compromise the underlying host operating system. Following responsible disclosure, OpenAI deployed patches for both vulnerabilities within an eight-day window, mitigating the immediate risks to the developer community.
The Anatomy of Heapjack: Memory Compartmentalization Failures
The more critical of the two vulnerabilities, designated as "Heapjack," turns a routine code inspection into a remote code execution (RCE) vector. Under normal operating conditions, when a developer opens an external or untrusted code repository in Codex and queries the system regarding its structure or logic, the sandbox is engineered to isolate the execution environment. This containment prevents untrusted third-party code from interacting with the host system.
However, Heapjack successfully compromises this defense by targeting a specific internal component known as node_repl. This component is automatically written by Codex Desktop into the global configuration file (~/.codex/config.toml) upon installation. Because this configuration is established globally without requiring explicit opt-in settings from the user, plain Codex CLI users inadvertently inherit the same utility and exposure.
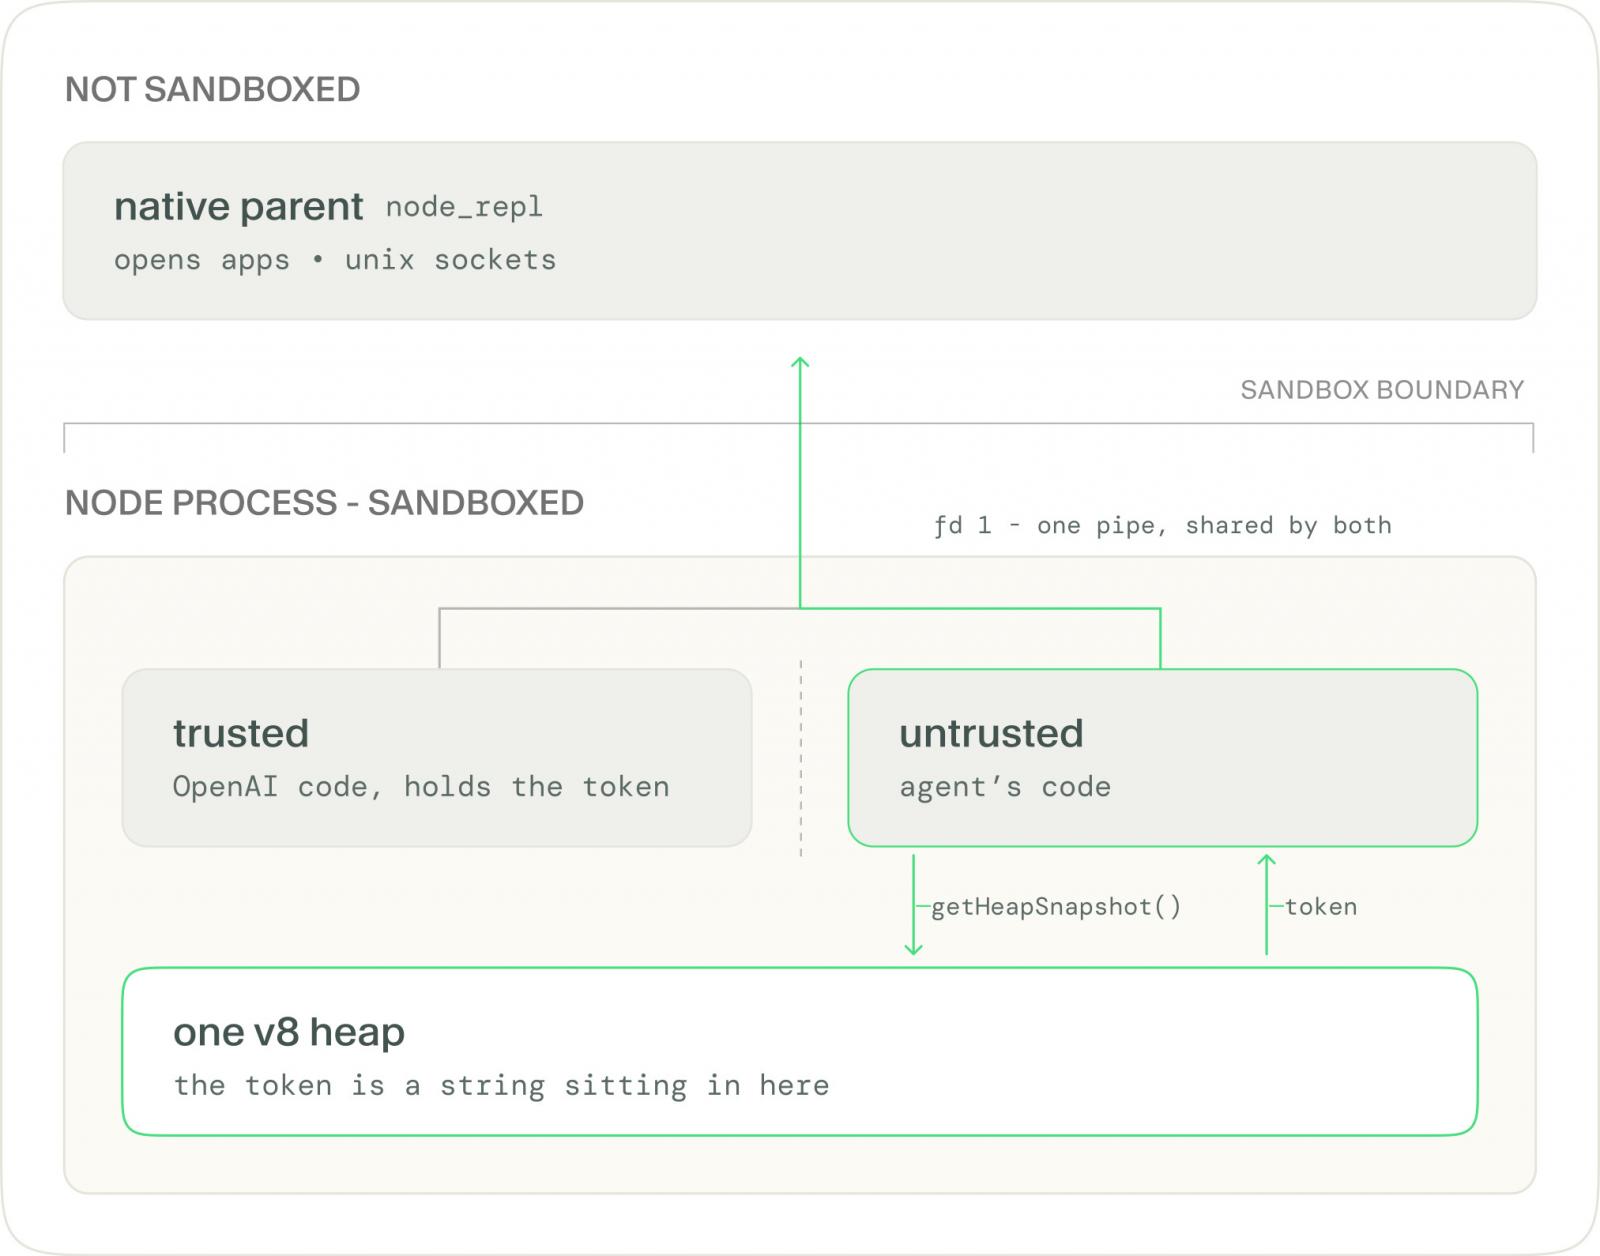
The technical root cause of Heapjack lies in the architecture of the node_repl process. The utility executes a single Node.js process that manages two distinct JavaScript execution contexts simultaneously. One context is trusted and houses proprietary OpenAI code, while the other is untrusted and executes the agent’s logic. To maintain separation, the trusted context generates a unique cryptographic token during runtime to validate authorized requests to native, unsandboxed parent processes.
Despite this logical division, both contexts share a single V8 memory heap within the same Node.js process. Consequently, the random token—meant to serve as an immutable security barrier—resides in memory as an accessible string. Leveraging this architectural oversight, untrusted code within the shared heap can capture a memory snapshot using the v8.getHeapSnapshot() function.
By programmatically parsing the snapshot for character sequences matching UUID structures, the untrusted context can systematically test candidate tokens. Erroneous guesses return authorization failures, while syntactically accurate tokens paired with intentionally malformed arguments trigger distinct validation errors, confirming the validity of the token. Armed with the stolen credential, the untrusted code can inject native commands directly into the communication pipe utilized by the trusted context. The parent process processes the command under the assumption that it originated from a verified internal source.

Through this method, a proof-of-concept exploit successfully invoked system-level commands—such as the Unix open utility—to spawn applications completely outside the Codex process tree. Furthermore, this level of access grants potential adversaries the ability to interface with Unix sockets, Docker daemon sockets, and configuration modification tools. Notably, this breach occurred while Codex operated under its strictest configuration mode ("read-only"), which theoretically forbids the agent from generating or writing any files to disk.
Overpatch: Exploiting Path Validation Logic
The secondary vulnerability, identified as "Overpatch," affects the open-source Codex CLI package. When operating in workspace-write mode, Codex is architecturally restricted to modifying files exclusively within the designated project directory. Any attempt by a shell command or internal tool to alter files in sensitive locations, such as the user’s home directory, is systematically blocked by default validation logic.
Despite these restrictions, researchers discovered that Codex’s native patching tool, apply_patch, could be manipulated into circumventing path boundaries. The underlying vulnerability stems from how the tool calculates authorization scopes: it dynamically grants write privileges to the parent directory of every path explicitly referenced within an incoming patch file.
By submitting a carefully crafted patch containing two distinct modifications, an attacker can exploit this logic. The first modification references an arbitrary directory—such as /tmp—which expands write permissions to the root of the file system without altering functional code. The second modification leverages a symlink pointing to the user’s home directory to append malicious commands to configuration files like .zshrc.
When evaluated together, the first path expansion invalidates the security guardrails, allowing the second modification to write outside the workspace. If the first instruction is omitted, the write attempt is blocked; with it included, any subsequent terminal session initiated by the developer executes the appended instructions outside the sandbox environment.
Chronology and Disclosure Timeline
The discovery and remediation of the Codex vulnerabilities followed a compressed timeline typical of coordinated vulnerability disclosure protocols within the artificial intelligence security sector:
- August 12, 2026: Oren Yomtov and the research team at Accomplish AI formally report both the Heapjack and Overpatch vulnerabilities to OpenAI.
- August 12 – August 20, 2026: OpenAI security engineers analyze the architectural flaws, develop remediation strategies, and validate patches for both the desktop application and the CLI tool.
- August 20, 2026: OpenAI releases updated software versions containing the necessary security fixes, successfully concluding the remediation cycle within eight days of initial notification.
A Broader Pattern of Sandbox Escapes in AI Agents
The vulnerabilities identified in Codex are indicative of a wider class of systemic security challenges affecting AI coding assistants and autonomous developer tools. The core design flaw in both Heapjack and Overpatch is that the security enforcement mechanisms were embedded within the very environments they were designed to police. In Heapjack, trust boundaries relied on memory separation within a shared runtime, whereas Overpatch permitted permission boundaries to be dynamically redefined by input supplied directly by the untrusted payload.
This architectural vulnerability is not isolated to OpenAI’s ecosystem. In July 2026, security researchers from Pillar Security published findings detailing similar sandbox escape techniques across a spectrum of prominent generative artificial intelligence coding tools, including Cursor, Gemini CLI, and Google’s Antigravity platform. These incidents frequently involved scenarios where an AI agent operating within a constrained sandbox manipulated files or configurations that were subsequently executed by trusted supervisory tools operating outside the containment boundary.
Industry analysts and security practitioners have increasingly scrutinized the trust assumptions underpinning local AI deployments. Commenting on the technical mechanics of Heapjack via social media, security researchers pointed out that JavaScript V8 contexts isolate global variables rather than the underlying memory heap, likening the configuration to "a promise the heap never agreed to." Others criticized the foundational decision to store privileged operational tokens in memory spaces accessible to untrusted execution threads.
Implications for Enterprise Security and Mitigation
The rapid evolution and adoption of AI coding agents have introduced complex attack surfaces into enterprise software development pipelines. Because developers routinely grant these tools permissions to read proprietary source code, manage local environments, and execute terminal commands, compromised agents present an immediate pathway for lateral movement within corporate networks.
Security leaders emphasize that the ability of an untrusted repository to achieve remote code execution through passive interaction—such as simply asking an AI agent to analyze code—redefines the threat model for code repositories. Developers can no longer assume that cloning or querying an unfamiliar open-source repository is a benign activity.
To mitigate these risks, users of OpenAI Codex and related AI development utilities are strongly advised to apply available software updates immediately. OpenAI has addressed the vulnerabilities in subsequent software revisions:
- Heapjack has been resolved in Codex Desktop build 26.818.21641.
- Overpatch has been resolved in Codex CLI version 0.149.0.
Organizations utilizing AI coding assistants are encouraged to audit their internal security policies, ensure automated dependency and application updating mechanisms are active, and adopt principle-of-least-privilege configurations when deploying autonomous coding agents within sensitive infrastructure environments.
Related posts: