New Malware Campaign Uses SEO-Optimized GitHub Repositories to Spread Rapuncel Infostealer and Terminate Antivirus Software

Security researchers from LastPass and Delphos Labs have uncovered a sophisticated and highly targeted malware campaign that weaponizes search engine optimization (SEO) techniques on GitHub to distribute a previously undocumented information stealer known as Rapuncel. The ongoing threat campaign, which meticulously impersonates at least 40 well-known software brands including the popular password manager LastPass, relies on a potent combination of malicious payloads, Microsoft-signed kernel drivers, and advanced evasion tactics to compromise victims, neutralize enterprise-grade security defenses, and siphon sensitive user data.
The discovery highlights an alarming evolution in how malicious actors acquire initial access and distribute payloads, increasingly exploiting trusted developer platforms and manipulating search engine algorithms to intercept users during routine software searches. As organizations and individual consumers alike grapple with the rising tide of sophisticated cyber threats, this campaign serves as a stark reminder of the persistent vulnerabilities inherent in modern digital supply chains and web discovery mechanisms.
The Attack Chain: From Search Engine to Compromised Endpoint
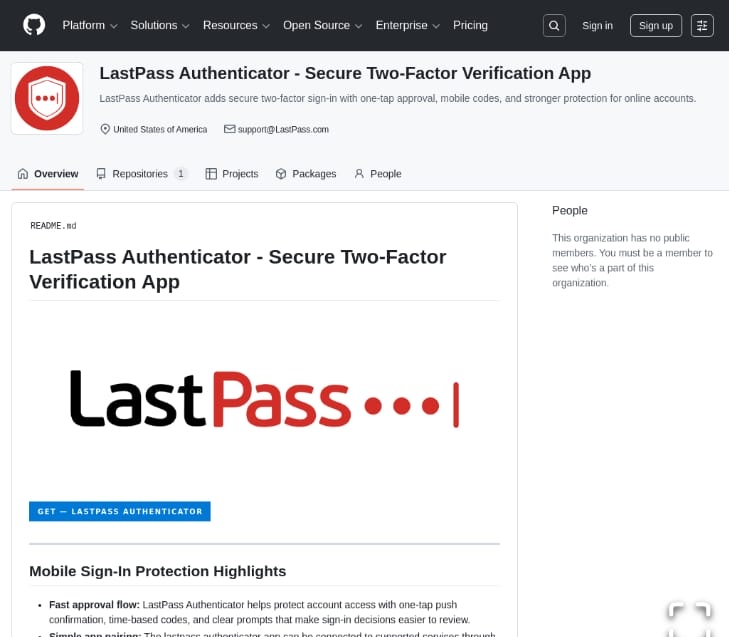
The malicious lifecycle begins well before a victim ever touches a line of code or visits a compromised repository. Threat actors orchestrate a calculated SEO poisoning campaign designed to push fraudulent GitHub repositories to the top of search engine result pages when users look for popular utilities, authenticators, and productivity software. Victims searching for tools such as the LastPass Authenticator are routinely redirected to deceptive GitHub pages meticulously crafted to mimic official, legitimate software repositories.
Upon navigating to these fraudulent pages, prospective victims are presented with prominent download buttons. Clicking these buttons initiates a complex chain of HTTP redirections intended to obfuscate the origin of the traffic and bypass basic network monitoring systems before ultimately landing on payload-delivery servers.
To circumvent automated security scans, cloud-based proxies, and heuristic endpoint detection systems, the attackers deliver heavily padded ZIP archives. These archives are artificially inflated with redundant data, bloating their file sizes to as much as 148 megabytes. Many traditional security solutions and web gateways bypass deep inspection on files exceeding certain size thresholds due to performance constraints, allowing the oversized archives to slip past perimeter defenses unnoticed.
Once downloaded and extracted, the archive deploys an installer that is, ironically, a direct copy of a legitimate Microsoft Visual Studio component—specifically, the CoreCLR Debugger, known commercially as ‘vsdbg.exe.’ The attackers rename this legitimate binary and configure it to perform DLL sideloading, forcing it to load a malicious dynamic-link library named ‘vsdbg.dll.’ This clever abuse of legitimate developer tools facilitates the simultaneous deployment of the Rapuncel infostealer and a highly dangerous kernel-level driver designated as ‘Alinubx.sys.’
Weaponizing Signed Kernel Drivers to Neutralize Security Software
Perhaps the most technically concerning aspect of the Rapuncel campaign is its deployment of a Microsoft-signed kernel driver designed explicitly to incapacitate endpoint detection and response (EDR) solutions and traditional antivirus products. Disguised as a legitimate NVIDIA system component named ‘nvfsflt64.sys,’ the driver registers itself within the Windows operating system as the NvFsFilter service, granting it deep system privileges.
According to technical analyses published by LastPass and Delphos Labs, the malicious driver functions as an aggressive EDR killer. It contains a hardcoded target list comprising 145 distinct antivirus, antimalware, and endpoint security products. When executed, the driver interacts directly with the Windows kernel to systematically terminate these defensive processes before they can detect or block the ongoing compromise.
The mechanism by which the driver defeats advanced operating system protections is particularly noteworthy. Researchers noted that the driver invokes the Windows kernel API function ObOpenObjectByPointer with the AccessMode parameter explicitly set to KernelMode. This technical maneuver effectively bypasses the standard user-mode security access checks (SeAccessCheck) normally enforced during handle-open operations.
By commanding the kernel to open targeted security processes directly as kernel-level code, the driver bypasses Protected Process Light (PPL)—the robust security architecture that modern Windows operating systems utilize to shield critical security components from tampering, even by users possessing administrative privileges.
Compounding the threat is the fact that the Alinubx.sys driver utilized in this campaign bears a valid digital signature through Microsoft’s official Windows Hardware Compatibility Publisher certificate chain. Furthermore, at the time of discovery, the specific driver variant had not yet been incorporated into Microsoft’s vulnerable driver blocklist. While the driver is primarily leveraged in this campaign for its destructive process-termination capabilities, security researchers also identified dormant code routines within the binary supporting file and registry hiding, arbitrary DLL injection, driver and process interception, network traffic manipulation, and port redirection, indicating that the threat actors retained the capability to expand the scope of their attack.
The Rapuncel Infostealer: Capabilities and Data Exfiltration
With all competing security software neutralized and rendered inert on the host machine, the Rapuncel infostealer initiates its primary mission: harvesting valuable user data and system intelligence.
Rapuncel systematically sweeps the infected device, gathering a wide array of sensitive information. While baseline infostealers typically target plaintext credentials, cookies, and system metadata, Rapuncel employs sophisticated extraction techniques designed to defeat modern browser security measures. Notably, to bypass the robust app-bound encryption protections implemented by Google Chrome, Microsoft Edge, and related Chromium-based browsers, the malware injects a specialized helper DLL directly into the target application and invokes its own custom Elevation Service to decrypt and extract protected credentials and session tokens.
Once the data harvesting phase is complete, Rapuncel compresses the stolen files into an archive and transmits them to an external command-and-control endpoint located at 2.26.126[.]50. The exfiltration occurs via an HTTP-formatted data transmission sent directly over raw TCP sockets, designed to blend in with routine web traffic or evade standard application-layer inspection tools.
To ensure long-term persistence across system reboots and administrative interventions, Rapuncel registers itself as a native Windows service. This persistence mechanism guarantees that even if a victim or automated recovery script restarts the compromised machine, any security tools that automatically reinitialize upon boot will be promptly detected and terminated by the resident malware before the infostealer executes its operational cycle.
Cryptographic and behavioral analysis conducted by LastPass and Delphos Labs suggests with moderate confidence that Rapuncel shares strong structural and operational ties to BoryptGrab, an established malware family. Additionally, researchers determined that the primary loader utilized to drop the infostealer was constructed using the Cruciferra PUROSANGUE commercial crypter, underscoring the attackers’ reliance on modular, off-the-shelf evasion tools.
Broader Implications and Enterprise Risk
This campaign underscores a troubling trend in contemporary cybercrime: the lowering technical barrier for executing sophisticated, multi-stage attacks through the abuse of trusted infrastructure. By exploiting GitHub—a platform universally relied upon by software engineers, system administrators, and everyday users—the threat actors leverage inherent user trust in developer ecosystems. Combined with search engine optimization tactics, this approach effectively transforms routine software acquisition into a high-risk vector for compromise.
Furthermore, the continued exploitation of signed legitimate drivers poses a persistent challenge for operating system vendors and security architects. While Microsoft maintains rigorous code-signing requirements and actively updates vulnerable driver blocklists, malicious actors continually discover and weaponize third-party drivers that slip through the verification cracks or leverage legitimate publisher chains improperly. This technique undermines the fundamental premise of driver signing, which assumes that cryptographic signatures equate to absolute trustworthiness.
The ability of the Alinubx.sys driver to bypass Protected Process Light (PPL) and disable up to 145 distinct security solutions highlights an escalating arms race between malware developers and endpoint security vendors. As EDR solutions become increasingly resilient, attackers are shifting their focus toward pre-execution kernel manipulation, effectively cutting the legs out from under host-based defenses before user-mode payloads ever touch the disk.
Guidance and Defensive Recommendations
In light of the active exploitation associated with the Rapuncel campaign, cybersecurity professionals and enterprise security teams are urging organizations and individual users to exercise heightened caution when downloading software from the internet.
Key defensive recommendations include:
- Strict Sourcing Policies: Users should strictly download applications, utilities, and packages directly from official vendor websites rather than relying on search engine results that lead to third-party repositories or community-driven code hosting platforms.
- Search Engine Vigilance: Individuals must remain wary of sponsored advertisements and promoted search results on major search engines, which are frequently leveraged by threat actors to push malicious links ahead of legitimate resources.
- Endpoint Monitoring and Behavioral Analysis: Enterprise security teams should ensure that their security monitoring tools are configured to detect unauthorized kernel driver installations, unusual DLL sideloading activities involving developer binaries such as
vsdbg.exe, and anomalous network connections attempting raw TCP exfiltration. - Regular Driver Blocklist Updates: Organizations should verify that their endpoint security platforms and operating systems are enforcing the latest Microsoft vulnerable driver blocklists to mitigate the risk of signed malicious drivers executing within the kernel ring.
As threat actors continue to refine their SEO poisoning methodologies and weaponize legitimate developer infrastructure, robust user awareness combined with defense-in-depth security architectures remains the most effective bulwark against sophisticated infostealer campaigns like Rapuncel.