Dutch Authorities Arrest Convicted Cybercriminal Linked to ShinyHunters as Syndicate Escalates Global Attacks

The landscape of international cybersecurity was jolted this month following a high-stakes law enforcement operation in the Netherlands, where authorities arrested a 24-year-old convicted cybercriminal suspected of providing critical infrastructure support to the prolific extortion syndicate known as ShinyHunters. The suspect, identified through multiple investigative sources as Pepijn van der Stap—formerly known in the cybercriminal underground by the handle “Umbreon”—was detained in mid-September. The arrest catalyzed a volatile reaction from remaining members of the hacker collective, who responded by launching a series of aggressive retaliatory operations, most notably breaching the Federal Bureau of Investigation’s recruitment portal and targeting the Russian-affiliated ransomware group Cl0p.
The unfolding crisis highlights an increasingly interconnected and treacherous ecosystem of global cybercrime, where elite hacking syndicates operate across fluid alliances, leveraging zero-day vulnerabilities, social engineering, and internal factional disputes to maximize both disruption and financial gain.
A Chronology of Escalation: From the Odido Breach to the FBI Hack
The trajectory leading to van der Stap’s arrest and the subsequent wave of retaliatory cyberattacks spans several months of intense international law enforcement and intelligence activity.
In February 2026, the Netherlands was targeted in one of its largest telecommunications breaches when a native Dutch speaker socially engineered an employee at Odido, the nation’s premier mobile provider. Tricked into authenticating through a spoofed web domain, the compromised employee granted intruders access to internal repositories containing the personal data of over 6.2 million Dutch citizens.
Throughout the spring and summer of 2026, ShinyHunters intensified its broader global campaign. By June, the group had begun weaponizing a critical security flaw in Oracle’s PeopleSoft software-as-a-service platform, cataloged as CVE-2026-35273. Although Oracle swiftly issued patches and major cybersecurity firms like Mandiant introduced mitigating firewall rules, the hackers successfully bypassed defenses using sophisticated URL-encoding techniques. This zero-day exploitation allowed them to harvest data from dozens of enterprise systems spanning technology, healthcare, government, and higher education sectors.

By early September, Dutch law enforcement escalated their public appeal, releasing an audio recording of the Odido telephone social engineering call to seek civilian assistance in identifying the operative. Shortly thereafter, on September 9, van der Stap participated in an interview with security journalists, presenting himself as a reformed technologist striving to make amends. However, communication abruptly ceased. Sources familiar with the investigation confirmed that Dutch authorities executed a raid on van der Stap’s residence on or around September 16, carting away hardware and placing him in custody for questioning.
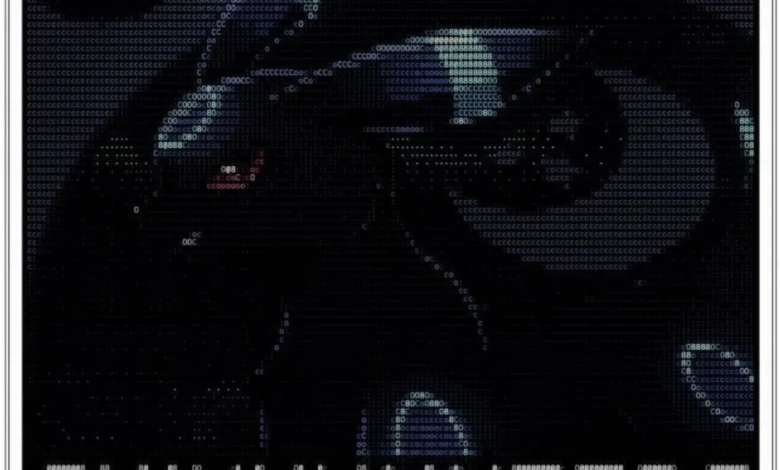
Within days of the detention, ShinyHunters launched a brazen cyberattack against the FBI’s applicant portal, apply.fbijobs.gov. The breach exposed sensitive personally identifiable information (PII)—including Social Security numbers, job titles, and detailed medical and psychiatric evaluations—of more than 5,000 bureau personnel, including special agents assigned to major cybercrimes and foreign state-backed threat units. The group left a defiant digital calling card on the compromised portal: an ASCII art rendition of the Pokémon character Umbreon paired with a message mocking law enforcement capabilities.
The Dual Identity of Pepijn van der Stap
The arrest of Pepijn van der Stap brings into sharp focus the paradoxical nature of modern cybercriminal profiles. Operating under the alias Umbreon, van der Stap previously built a notorious reputation by accumulating massive troves of stolen databases, leveraging forums like RaidForums and Breached to extort victims. His initial criminal enterprise, prosecuted in late 2023, yielded illicit proceeds estimated between €1.5 million and €2.7 million.
Despite his illicit activities on English-language hacking communities, van der Stap simultaneously maintained a legitimate professional footprint in the mainstream cybersecurity industry. By day, he functioned as a software engineer for the Amsterdam-based security startup Hadrian and volunteered his technical expertise with the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit organization dedicated to uncovering systemic vulnerabilities.
Following his 2023 conviction, van der Stap was sentenced to four years in prison, with one year suspended. Citing a need for structured psychological support to manage post-traumatic stress disorder stemming from childhood trauma, he initially opted to remain incarcerated. He was ultimately released in December 2025. At the time of his September 2026 detention, he was employed as an offensive security lead at Neo Security, while continuing to navigate civil litigation and financial restitution orders stemming from his prior convictions.
During legal proceedings and subsequent interviews, van der Stap maintained that his primary driver was not financial enrichment, but an obsessive compulsion toward digital data collection and organization.

Internal Fractures and the Rise of "Rey"
The dramatic pivot in ShinyHunters’ operational tempo—highlighted by high-risk attacks against the FBI and Russian ransomware syndicates—reflects a significant internal power shift within the collective. Industry intelligence suggests that control of the ShinyHunters brand has shifted toward a teenage cybercriminal operating out of Amman, Jordan, known by the alias "Rey."
Rey is reportedly a key administrator within ScatteredLapsussHunters (SLSH), an aggressive hybrid syndicate fusing elements of Scattered Spider, LAPSUS$, and ShinyHunters. The alliance between these factions had previously experienced friction following a joint operation earlier in the year involving TeamPCP, a supply-chain hacking group whose stolen credentials were rapidly burned when security analysts covertly fed access keys to major cloud infrastructure providers like Amazon and Microsoft.
As trust eroded among the allied groups, internal conflicts intensified. Security researchers note that the inclusion of the oversized Umbreon Pokémon branding in the FBI job portal defacement was not merely a nostalgic homage, but a calculated maneuver by Rey to intentionally implicate van der Stap in the high-profile attack and deflect law enforcement scrutiny away from the true architects of the breach.
Official Responses and Law Enforcement Acknowledgment
As international agencies race to contain the fallout from the global campaign, official statements from targeted institutions and law enforcement have confirmed the gravity of the breaches.
The Federal Bureau of Investigation issued a formal statement acknowledging the unauthorized access to its job portal and the subsequent exposure of employee data, assuring the public that mitigation protocols were deployed immediately upon detection. Meanwhile, the Dutch police officially confirmed the arrest of a 24-year-old suspect in connection with the ongoing ShinyHunters investigation. Authorities announced that the detainee is scheduled to appear before the chambers of the Rotterdam District Court to face formal questioning regarding his alleged facilitation of the syndicate’s infrastructure and extortion schemes.
In stark contrast, ShinyHunters leadership issued volatile statements via encrypted messaging channels, dismissing the competency of Dutch law enforcement and vowing full emotional, mental, and financial support—including legal defense funding—for their detained associate.

Broader Implications for Enterprise and National Security
The events surrounding the dismantling of van der Stap’s alleged network and the subsequent aggression of the ShinyHunters syndicate underscore critical vulnerabilities in global supply chains and digital security infrastructure.
Security analysts emphasize that the exploitation of enterprise software platforms like Oracle PeopleSoft demonstrates how sophisticated cybercriminal organizations continually adapt to bypass traditional defensive perimeters. Furthermore, the convergence of disparate underground factions under volatile leadership figures like Rey signals an era of heightened unpredictability in ransomware and extortion tactics.
As organizations worldwide grapple with the fallout of the PeopleSoft mass-exploitation campaign—projected by threat intelligence firms to drive nearly $100 million in illicit extortion revenue through the course of 2026—the case serves as a stark reminder of the persistent convergence between legitimate technological expertise and underground cybercrime.