AI-Driven Cyberattacks Surge as Threat Actors Industrialize Offensive Operations Across Japan and Beyond

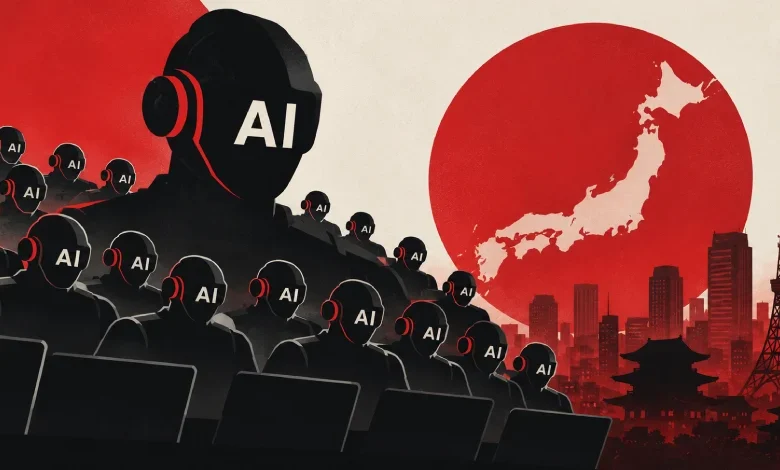
The global cybersecurity landscape is undergoing a profound transformation as malicious actors increasingly transition from manual exploitation to the deployment of autonomous and AI-assisted frameworks. Recent forensic disclosures from TrendAI have brought to light three distinct cyber campaigns targeting Japanese organizations, illustrating how artificial intelligence is being utilized as a critical "force multiplier." These operations, which range from fully autonomous agentic workflows to human-in-the-loop LLM-assisted exploitation, represent a new, dangerous maturity in the cybercrime ecosystem where speed, scale, and language localization are no longer barriers to entry.
The Anatomy of AI-Enhanced Campaigns
TrendAI’s analysis of compromised server environments has unveiled a spectrum of AI integration. Researchers Bakuei Matsukawa and Joseph C. Chen noted that while some attackers still rely on traditional, hand-operated workspaces, others have successfully migrated to AI-agent platforms capable of automating the entire kill chain. This shift moves away from the bespoke, artisanal nature of past breaches toward a structured, industrial-scale methodology.
In the first identified campaign, attackers deployed the open-source penetration testing tool CyberStrikeAI. The activity, concentrated in October 2026, demonstrated a high level of operational efficiency. The framework utilized 44 specialized agents to handle the granular components of the attack lifecycle: reconnaissance, vulnerability discovery, validation, exploitation, command-and-control (C2) establishment, data exfiltration, and automated reporting. Crucially, the system enabled the creation of high-fidelity, Japanese-language phishing templates and fake login portals, effectively neutralizing one of the most reliable indicators of a foreign-based intrusion—linguistic inaccuracy.
The second case study highlights a hybrid model: human-led orchestration bolstered by Large Language Models (LLMs). This campaign specifically sought to exploit AI workflow platforms and inference services, likely to secure high-performance computing power for future malicious activities at a minimal cost. This operation, which persisted for 24 days between August and September 2026, targeted a geographic information system (GIS) server. By leveraging default credentials, the actors exfiltrated sensitive cadastral data, commercial records, and internal email communications, signaling that attackers are increasingly treating AI inference infrastructure as a primary, rather than secondary, objective.

The third instance reflects a more constrained use of AI, where the technology served as a tool-building assistant. By using AI to develop scripts and refine exploitation techniques, the threat actors successfully targeted edge devices—including hardware from Cisco, Citrix, F5, and Yamaha. These campaigns, occurring between January and October 2026, demonstrate a focus on opportunistic exploitation of known vulnerabilities, where the AI’s primary contribution was to accelerate the speed at which an experienced operator could iterate through targets.
Chronology of Escalating AI-Integrated Threats
The 2026 calendar year has marked a pivotal turning point in the adoption of offensive AI:
- January – October 2026: A series of six campaigns targeting edge devices and WebLogic servers occurs globally, including in the UK, France, Italy, Qatar, and Colombia, utilizing AI-assisted scripting.
- August – September 2026: A 24-day campaign targets Japanese GIS infrastructure, utilizing LLMs to aid human operators in data exfiltration and resource theft.
- October 2026: A surge in activity involving CyberStrikeAI, impacting 19 organizations—16 of which were based in Japan.
- Late October 2026: Microsoft reports that the China-aligned actor Storm-0940 utilized the ARTEX framework to compromise over 2,250 Microsoft 365 tenants via a ConnectWise backup application.
- October 2026: South Korean authorities identify a network of seven suspects who utilized the ARTEX framework to breach 90 organizations, resulting in the theft of 8.2 million records and attempted ransom demands totaling $270,000.
The Commoditization of Cybercrime
The proliferation of offensive AI is not occurring in a vacuum. A growing underground economy has emerged, centered on the sale of stolen AI session tokens and pre-packaged offensive tools such as APEX AI, MessiahGPT, and DarkGPT. These tools lower the barrier to entry, allowing less sophisticated actors to execute attacks that previously required the expertise of a high-tier Advanced Persistent Threat (APT) group.
The impact of this commoditization is evident in the recent activities of actors like Storm-0940. By utilizing agentic AI tools, the group achieved privileged cloud persistence across a massive target set in a remarkably short timeframe. This represents a fundamental shift: the "workforce" of a threat actor is now effectively augmented by AI agents that can work without fatigue, adapt to local languages in real-time, and test thousands of vulnerabilities simultaneously.
Strategic Implications and Defensive Challenges
Industry consensus suggests that AI has not introduced entirely new categories of exploitation but has instead optimized the efficiency of existing ones. According to the Microsoft 2026 Digital Defense Report, the median time from the discovery of a security vulnerability to its weaponization has collapsed to under 24 hours. This rapid cycle leaves little room for traditional patch management and human-led incident response.

Rapid7 researchers have emphasized that AI acts as both a "force multiplier" and an "expanding attack surface." As organizations rush to integrate AI into their own operations, they inadvertently provide new targets for adversaries. Furthermore, the reliance on AI to automate decision-making creates a "speed trap" for defenders. While organizations can use AI to monitor and block threats, the attackers’ ability to rapidly iterate their tactics means that defenders must be prepared to respond at machine speed.
The consensus among cybersecurity analysts at firms like Trend Micro is that access to "frontier" AI models is not the sole requirement for success. Rather, it is the depth of the ecosystem—the ability to reliably and independently sustain the attack at scale—that determines the efficacy of the threat actor. As AI becomes an embedded, operational component of APT campaigns, the focus of defense must shift from purely technical indicators of compromise (IoCs) to behavioral analysis and the securing of the underlying AI infrastructure itself.
Addressing the Policy and Operational Gap
The incident involving the South Korean network and the 32-year-old mastermind highlights the human factor that remains at the center of these automated operations. Even with the most advanced AI tools, attackers still require a foundation of traditional cybersecurity knowledge. The suspect’s history in professional penetration testing suggests that AI is most dangerous when paired with the tactical intuition of a seasoned operator.
Looking forward, the global security community is grappling with how to regulate the development of offensive AI tools without stifling legitimate research. The current climate suggests that the "democratization" of these tools is outpacing policy efforts. As threat actors continue to industrialize social engineering, automate reconnaissance, and refine malicious scripts, the distinction between a state-sponsored actor and a cybercriminal syndicate continues to blur.
Organizations are advised to prioritize the hardening of exposed edge devices, the implementation of robust identity and access management (IAM) to prevent the type of privileged persistence seen in the Storm-0940 case, and a transition toward proactive, AI-driven threat hunting. As the "median time to exploit" continues to shrink, the capacity for organizations to detect and neutralize threats in the early stages of the kill chain will be the defining factor in their digital resilience. The era of manual defense is drawing to a close; in its place, a new, automated arms race has begun.